CompTIA Security+ practice test — with hands-on labs, not just flashcards
Most CompTIA Security+ prep stops at multiple-choice questions. CrushCert adds hands-on labs built like the exam’s PBQs — the drag-and-drop and troubleshooting questions most people fail on — alongside 400+ adaptive practice questions and a full timed mock exam. Call it Security+, Security Plus or Sec+ — everything for the exam is here, in one place.
7 days free · No card required · Built to pass you on the first try
Exam update: Security+ V8 (SY0-801) launches Nov 17, 2026; SY0-701 stays available until Jun 11, 2027. CrushCert covers both: pick SY0-701 or SY0-801 on your dashboard and every quiz, flashcard and mock exam follows the version you are sitting. See what changes and which version to take →
How CrushCert gets you exam-ready
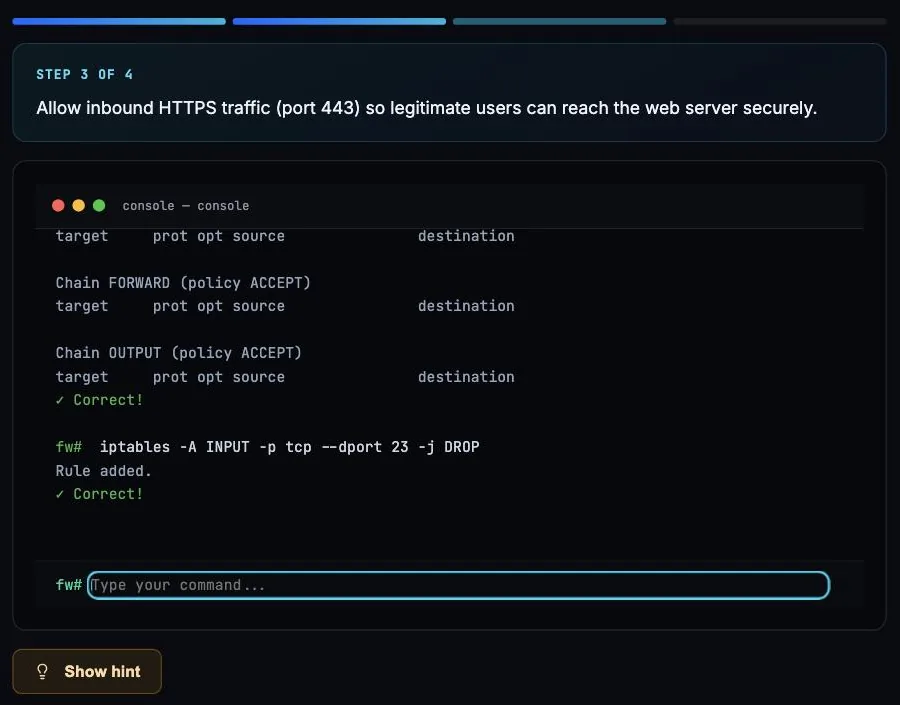
Hands-on labs
Drag-and-drop to match concepts and work through real troubleshooting scenarios — exactly the performance-based tasks the exam throws at you, not just multiple choice.
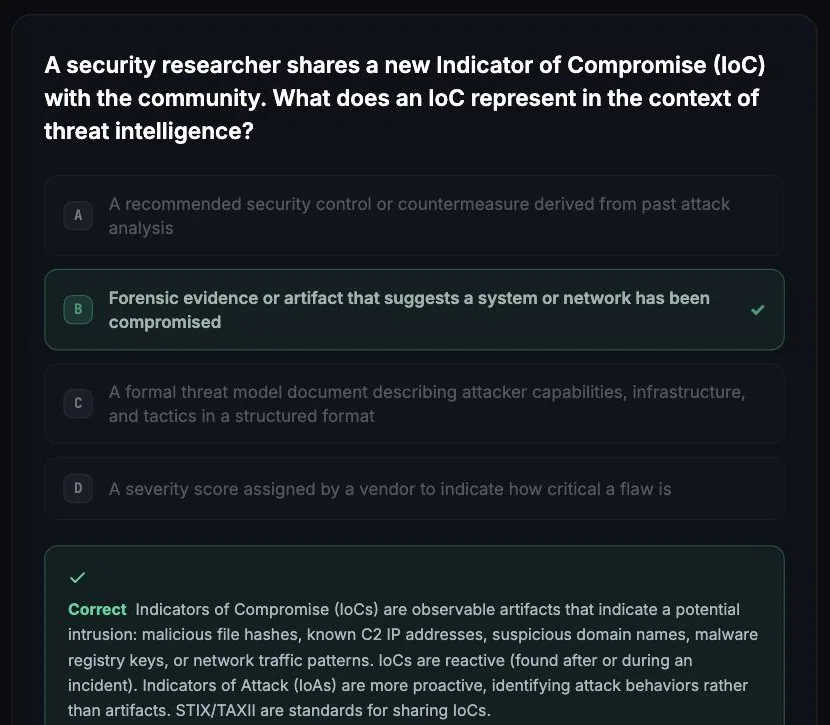
Adaptive practice
The algorithm tracks every question you miss and serves more of those topics, so your weak areas get more reps and every session moves your score.
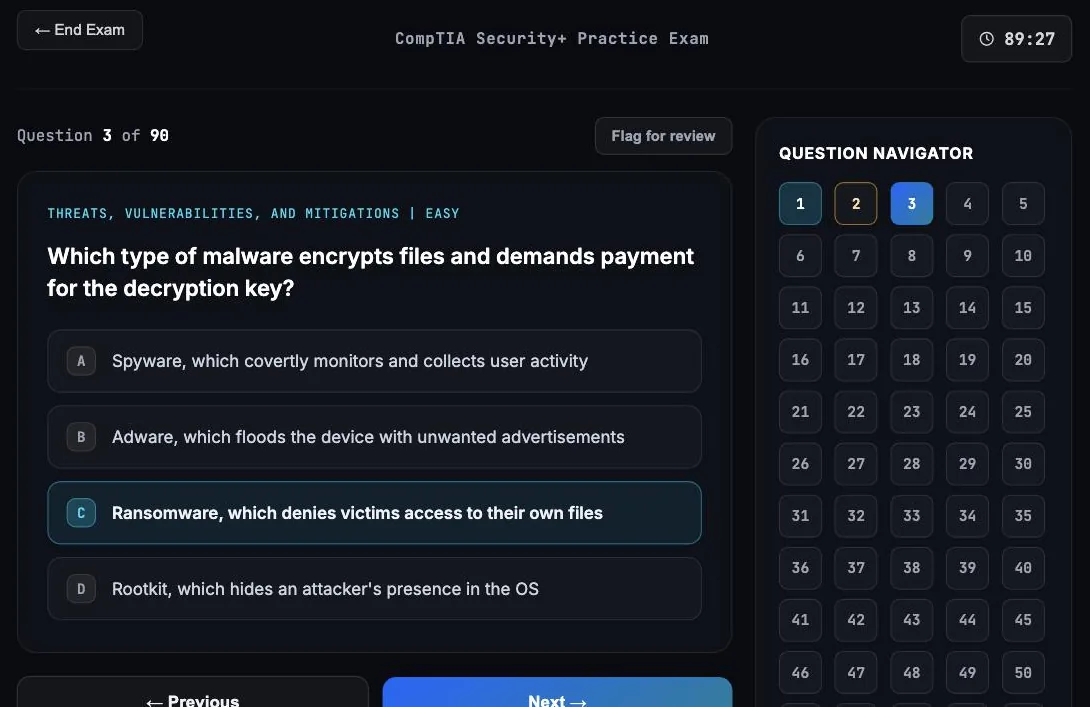
Realistic mock exams
Full-length, timed tests that mirror the real exam — countdown timer, question navigator, mark-for-review, and a 83% pass line so you know you're ready before exam day.
What studying looks like
Real screens from the Security+ track, not mockups.
What's on the CompTIA Security+ exam
The Security+ (SY0-701) has up to 90 questions in 90 minutes, scored on a 100–900 scale with a 750 passing score, and costs about $425. The five domains and weightings:
| Domain | Weight |
|---|---|
| General Security Concepts | 12% |
| Threats, Vulnerabilities & Mitigations | 22% |
| Security Architecture | 18% |
| Security Operations | 28% |
| Security Program Management & Oversight | 20% |
CrushCert's question bank and labs map to every domain. Hands-on lab and topic coverage includes:
Train on every domain above
Adaptive practice questions and hands-on labs mapped to these exact domains. 7 days free, no card required.
Start free trialFree CompTIA Security+ practice questions: are you ready?
Ten questions across all five exam domains. Answer each one, see the explanation, and find out which topic to work on first. No account needed.
Free readiness check
RSA uses a public/private key pair, making it asymmetric. AES, 3DES, and Blowfish are symmetric algorithms. Every CrushCert question includes an explanation like this.
A DDoS (Distributed Denial of Service) attack uses many compromised systems — a botnet — to overwhelm a target. A plain DoS comes from a single source.
TLS encrypts traffic between browsers and servers — this is what puts the "S" in HTTPS. FTP, SNMP, and Telnet are unencrypted by default.
Event ID 4728 records when a user is added to a security-enabled global group, such as Domain Admins. Monitoring this event is critical for detecting unauthorized privilege escalation. Event 4729 = removal from global group; 4725 = account disabled; 4727 = security-enabled global group created.
A risk management framework such as NIST RMF or ISO 31000 provides the overall structure for identifying, assessing, and responding to risk. The others address narrower, specific concerns.
GDPR governs personal data of EU residents — consent to collect, the right to erasure, and mandatory breach notification. HIPAA covers health data, SOX financial reporting, and PCI DSS card data.
Whaling targets senior executives or high-profile individuals with carefully crafted phishing attacks. Spear phishing targets specific individuals but not necessarily executives. Smishing is phishing delivered by SMS text message and vishing is phishing by voice call; both describe the delivery channel, not the target, and neither is specific to high-ranking individuals.
A CA is a trusted entity that issues digital certificates, binding a public key to an identity. It forms the trust foundation of PKI (Public Key Infrastructure). Negotiating session keys is the job of protocols like TLS, not the CA; hashing and salting credentials is password storage handled by the directory or application; detecting unauthorized access is an IDS/IPS function. A CA only vouches for identities by signing certificates.
TTPs describe the behavior of threat actors: Tactics (the 'why' — the goal), Techniques (the 'how' — the method), and Procedures (the specific implementation details). Understanding TTPs helps predict and defend against attacks. Tunneling transport protocols, trusted third-party certificate validation services, and threat telemetry parameters are invented expansions; none of them is an actual meaning of TTPs in threat intelligence.
A honeypot is a decoy system designed to attract attackers. Security teams use honeypots to study attack techniques, detect intrusions, and divert attackers from real systems. Replicating server data offsite is backup and disaster recovery; inspecting and blocking malicious HTTP requests is the role of a web application firewall; and isolating password hashes in a vault is a credential storage control — none involve luring attackers to a decoy.
Why learners pick CrushCert
You practice the way the exam tests you. The exam includes performance-based and scenario items — not just recall. Prep that's only flashcards leaves you guessing on test day. CrushCert's labs put you in the driver's seat.
Pay for one exam or all of them. Security+ alone is $10/month; the Associate plan is $19/month and covers CCNA, CompTIA A+, Network+, Security+, Azure Fundamentals, and several AWS exams — so if you're stacking certs, it's all included.
You always know your readiness. A live readiness score blends your quiz accuracy, mock results, and lab performance, and points you to exactly what to study next.
A guided plan tells you what to study today. Guided Learning builds a short daily plan from your performance — a warm-up review, a lesson on your weakest topic, flashcards, and a hands-on lab, all in about 20 minutes, with spaced repetition so material comes back right before you'd forget it.
Keep learning: CompTIA guides & path
Best Security+ practice tests in 2026
Professor Messer, Jason Dion, CertMaster, CrushCert and more — SY0-701 practice tests compared honestly.
STUDY PLANHow long to study for Security+ (SY0-701)
Realistic timelines by experience level, total study hours, and a week-by-week 6-week plan.
CAREERIs CompTIA Security+ worth it in 2026?
The jobs it opens, DoD approval, cost, difficulty, and study time — plus who should take it.
EXAM UPDATESY0-801 vs SY0-701: which should you take?
SY0-801 launches Nov 17, 2026; SY0-701 retires Jun 11, 2027. New weights, the new AI objective, and a simple decision rule.
NEXT STEPCompTIA SecAI+: secure AI systems
CompTIA's new AI security cert builds directly on Security+ — prompt injection, the OWASP LLM Top 10, securing AI agents, and AI governance.
Continue your CompTIA path — CrushCert also covers A+, Network+, CySA+, CASP+ / SecurityX, and SecAI+, all in one plan.
Ready to crush the CompTIA Security+?
Adaptive questions, hands-on labs, and full mock exams — start free for 7 days, no card required.
Start studying freeCompTIA Security+ FAQ
How many questions are on the Security+ exam?
The SY0-701 has up to 90 questions in 90 minutes, including multiple-choice and performance-based items.
Does CrushCert include hands-on Security+ labs?
Yes — drag-and-drop and troubleshooting scenarios covering cryptography, access control, network security, and incident response, matching the exam's performance-based questions.
What score do you need to pass Security+?
750 on a 100–900 scale. CrushCert mock exams use an 83% pass line so your practice matches the real bar.
How long does it take to study for Security+?
Typically 1–3 months, less with prior IT experience. CrushCert's weak-area targeting focuses your time where it counts.