CompTIA CySA+ practice test — with hands-on labs, not just flashcards
Most CompTIA CySA+ prep stops at multiple-choice questions. CrushCert adds hands-on labs built like the exam’s PBQs — the drag-and-drop and troubleshooting questions most people fail on — alongside 300+ adaptive practice questions and a full timed mock exam. Call it a CySA+ or CySA practice test — everything for the exam is here, in one place.
7 days free · No card required · Built to pass you on the first try
How CrushCert gets you exam-ready
Hands-on labs
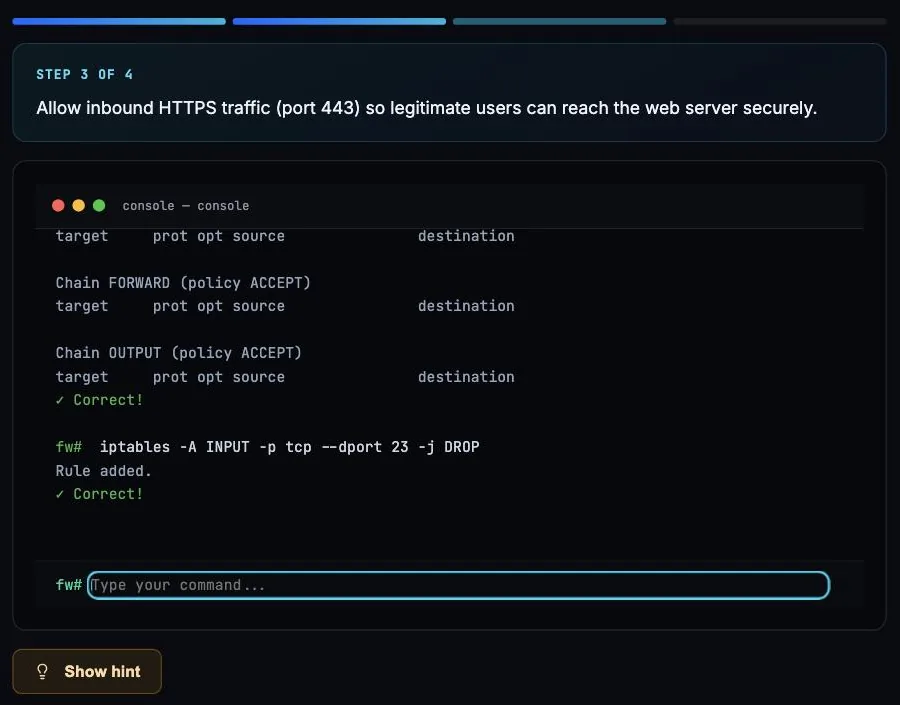
Drag-and-drop to match concepts and work through real troubleshooting scenarios — exactly the performance-based tasks the exam throws at you, not just multiple choice.
Adaptive practice
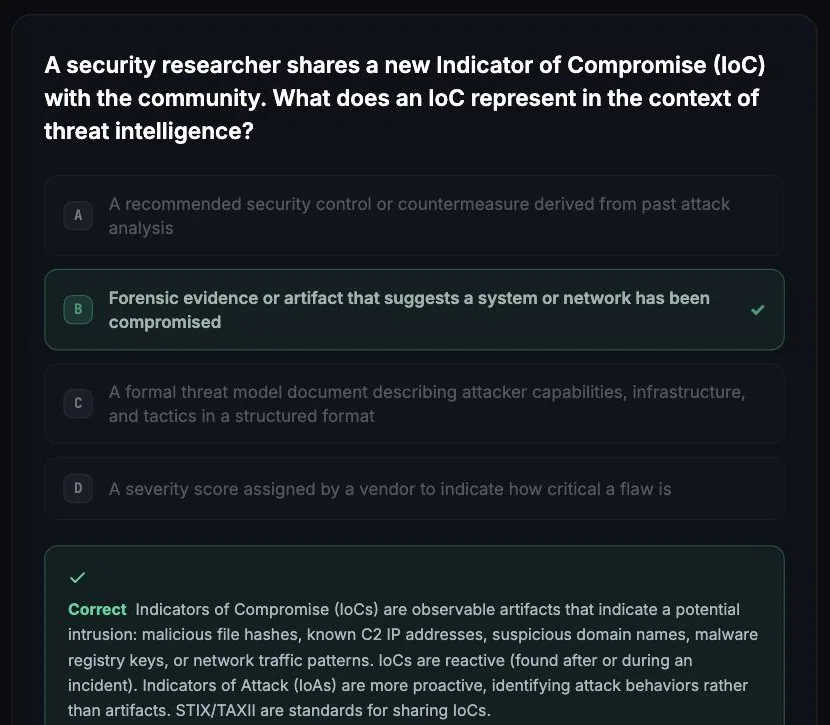
The algorithm tracks every question you miss and serves more of those topics, so your weak areas get more reps and every session moves your score.
Realistic mock exams
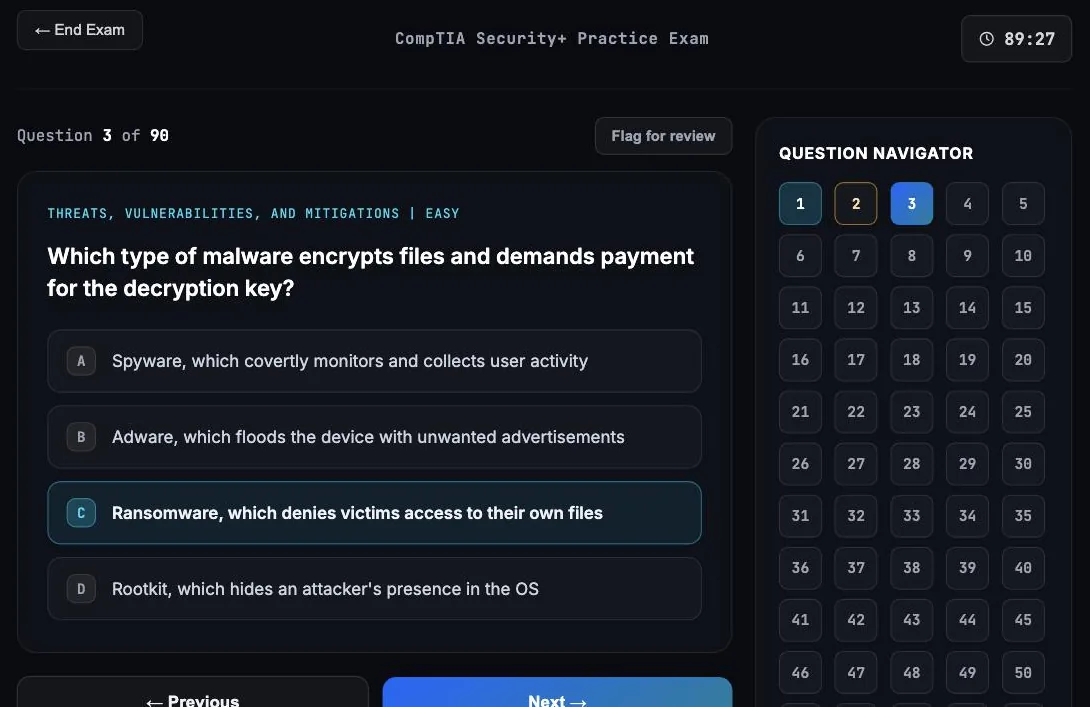
Full-length, timed tests that mirror the real exam — countdown timer, question navigator, mark-for-review, and a 83% pass line so you know you're ready before exam day.
What studying looks like
Real screens from CrushCert's CompTIA track (shown: Security+), not mockups.
What's on the CompTIA CySA+ exam
The CySA+ CS0-004 (launched June 2026) has up to 85 questions in 165 minutes, scored on a 100–900 scale with a 750 passing score, and costs about $392. The four CS0-004 domains and weightings (CS0-003 used 33/30/20/17):
| Domain | Weight |
|---|---|
| Security Operations | 34% |
| Vulnerability Management | 26% |
| Incident Response & Management | 24% |
| Reporting & Communication | 16% |
CrushCert's question bank and labs map to every domain. Hands-on lab and topic coverage includes:
Train on every domain above
Adaptive practice questions and hands-on labs mapped to these exact domains. 7 days free, no card required.
Start free trialFree CompTIA CySA+ practice questions: are you ready?
Ten questions across all four exam domains. Answer each one, see the explanation, and find out which topic to work on first. No account needed.
Free readiness check
A SIEM (Security Information and Event Management) platform aggregates and correlates logs and events for monitoring and detection. Every CrushCert question includes an explanation like this.
The CVSS temporal score adjusts the base score based on factors that change over time, including exploit code maturity (whether public exploits exist) and remediation level.
After containment, eradication removes the threat (malware, compromised accounts, backdoors) from the environment before recovery can begin.
MTTD measures the average time between when a threat occurs and when the security team becomes aware of it, reflecting the effectiveness of detection capabilities.
Defense in depth layers multiple security controls (firewalls, IPS, endpoint protection, access controls) so that if one layer fails, others continue to provide protection.
Low-severity findings should be risk-ranked by the criticality of affected assets, grouped into batches, and addressed during regular maintenance cycles rather than ignored or panic-fixed.
Incident priority is determined by combining the severity of the incident's impact with how critical the affected systems are to business operations.
Leadership cannot assess shadow AI risk without knowing which tools are in use and what data they receive, so an inventory comes first. That inventory then supports policy and blocking decisions.
Log normalization transforms logs from different sources (firewalls, servers, applications) into a common format, enabling consistent searching, correlation, and analysis.
SCAP (Security Content Automation Protocol) is a suite of specifications for standardizing vulnerability management, security measurement, and compliance checking.
Why learners pick CrushCert
You practice the way the exam tests you. The exam includes performance-based and scenario items — not just recall. Prep that's only flashcards leaves you guessing on test day. CrushCert's labs put you in the driver's seat.
Pay for one exam or all of them. CySA+ alone is $15/month; the Professional plan is $24/month and covers the CCNP core exams, AWS Solutions Architect and SA Pro, CySA+, CASP+/SecurityX, and SecAI+ — so if you're stacking certs, it's all included.
You always know your readiness. A live readiness score blends your quiz accuracy, mock results, and lab performance, and points you to exactly what to study next.
A guided plan tells you what to study today. Guided Learning builds a short daily plan from your performance — a warm-up review, a lesson on your weakest topic, flashcards, and a hands-on lab, all in about 20 minutes, with spaced repetition so material comes back right before you'd forget it.
Keep learning: CompTIA guides & path
Best CompTIA CySA+ practice tests in 2026
Jason Dion, CertMaster, Whizlabs, Pearson Test Prep, and CrushCert compared honestly for CS0-004.
CAREERIs CompTIA CySA+ worth it in 2026?
Jobs, salary reality, cost, and where CySA+ fits vs Security+ — who should get it and who shouldn't.
NEXT STEPCompTIA SecAI+: secure AI systems
Bring your SOC skills to AI — using AI in security operations, defending against AI-driven attacks, and securing LLM apps and agents.
Continue your CompTIA path — CrushCert also covers A+, Network+, Security+, CASP+ / SecurityX, and SecAI+, all in one plan.
Ready to crush the CompTIA CySA+?
Adaptive questions, hands-on labs, and full mock exams — start free for 7 days, no card required.
Start studying freeCompTIA CySA+ FAQ
How many questions are on the CySA+ exam?
CS0-004 (like CS0-003) has up to 85 questions in 165 minutes, including multiple-choice and performance-based items.
Does CrushCert include hands-on CySA+ labs?
Yes — analysis and troubleshooting scenarios covering log/SIEM analysis, threat detection, vulnerability management, and incident response.
What score do you need to pass CySA+?
750 on a 100–900 scale. CrushCert mock exams use an 83% pass line so your practice matches the real bar.
How long does it take to study for CySA+?
Typically 2–4 months, often after Security+. CrushCert's readiness score tells you when you're ready.